Zero-Trust Egress: Why Butlers Reach Developer APIs Only Through Life Butler
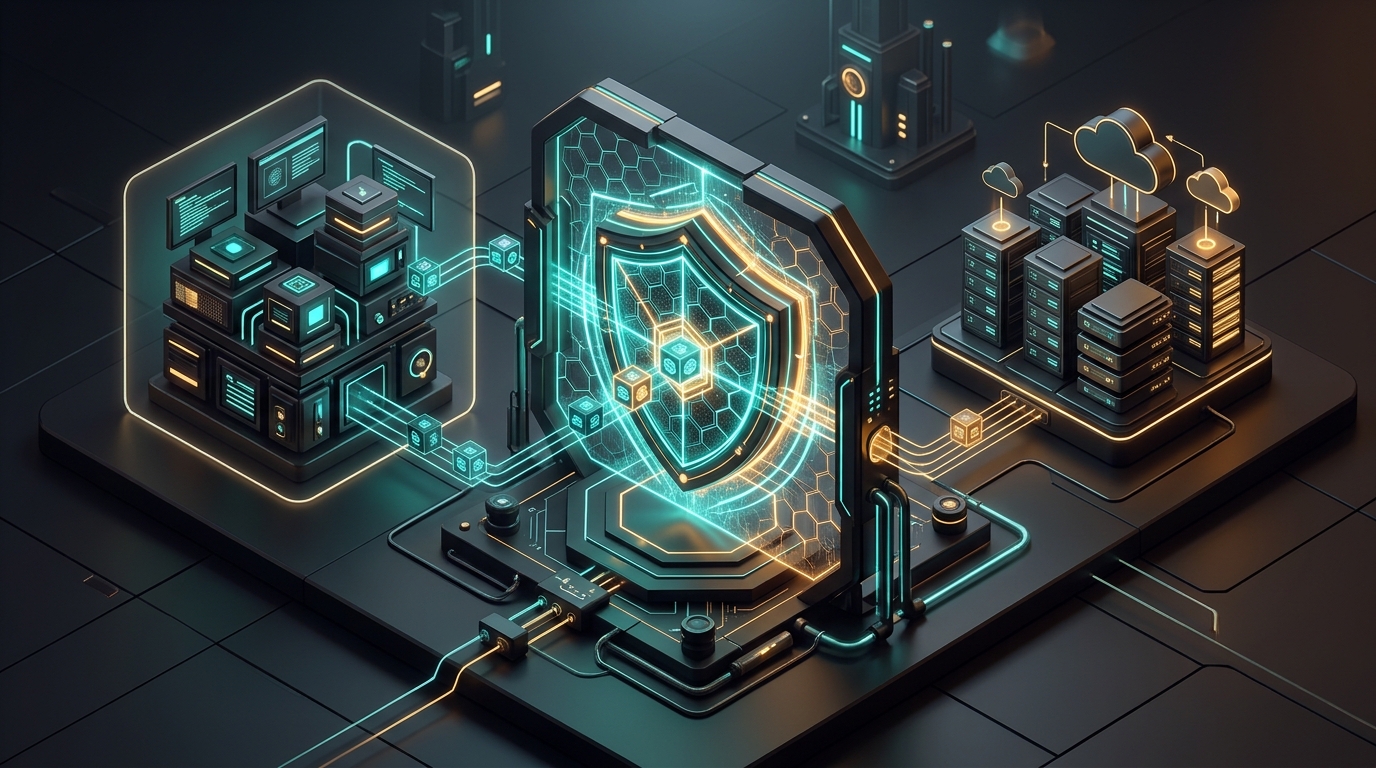
A core tenet of Life Butler is absolute privacy: a Butler bundle runs in an isolated frame with no access to local storage, no ambient cookies, and zero network access. It physically cannot phone home. But what happens when a developer builds a fitness Butler that syncs with their gym booking system, or a financial Butler that fetches exchange rates?
In traditional ecosystem models—from web browser extensions to IDE plugins—giving an extension network access means granting it raw, unmonitored egress. An add-on with network permission can exfiltrate sensitive data, track user telemetry in the background, or phone home to arbitrary endpoints.
This week, we ratified and deployed our architectural answer: Mediated Remote Calls Through Life Butler (ADR BUTLER-2026-10-25-remote-calls-through-life-butler). A Butler still possesses zero direct network capabilities. When it needs its developer's server, Life Butler acts as an authenticated, sanitizing proxy.
Architectural Evaluation: Four Egress Paradigms
When deciding how third-party Butlers interact with external developer servers, we weighed four competing patterns against our privacy commitments:
- •Direct Egress: Allowing direct
fetch()to external origins leaves Life Butler blind to payload contents, request frequency, and exfiltration attempts. - •Framed Web Embeds: Framing a developer-hosted URL means code can mutate after staff review, invalidating approval guarantees.
- •Identity Leakage: External servers can fingerprint browser attributes, IP addresses, and session timings directly.
- •No Kill Switch: Compromised add-on backends cannot be paused immediately across all clients.
- •Zero-Network Frame: The Butler frame remains completely disconnected from the Internet; calls route via Bridge v1.
- •DNS Proof of Ownership: Origin must be verified via a DNS TXT challenge in the Developer Portal.
- •Pseudonymous User IDs: Developers receive an opaque per-Butler user identifier, never your email, name, or master ID.
- •Instant Server-Side Kill Switch: Staff can sever external egress for any compromised Butler in milliseconds.
End-to-End Relay Topology
Every remote call is mediated through Life Butler's hardened edge relay. No browser cookies, auth tokens, or internal network headers ever cross the boundary:
┌───────────────────────────────────────┐
│     Sandboxed Butler Frame (Offline)  │
│     bridge.remote.call('/sync', data) │
└──────────────────┬────────────────────┘
                   │ MessageChannel (postMessage)
                   ▼
┌───────────────────────────────────────┐
│          Host App Shell               │
│     • Enforce user consent grant      │
│     • Dispatch to Life Butler Backend │
└──────────────────┬────────────────────┘
                   │ HTTPS POST /v1/relay
                   ▼
┌─────────────────────────────────────────────────────────────┐
│                 Life Butler Edge Relay                      │
│  1. Verify active user consent & origin whitelist           │
│  2. Scrub ambient headers & resolve IP (anti-SSRF)          │
│  3. Inject HMAC signature & pseudonymous sub_butler_xxx ID  │
│  4. Enforce rate limit (100 req/min) & payload cap (256 KB) │
└──────────────────┬──────────────────────────────────────────┘
                   │ Signed HTTPS POST
                   ▼
┌─────────────────────────────────────────────────────────────┐
│             Developer's Verified Origin                     │
│  • Verify X-LifeButler-Signature (HMAC-SHA256)              │
│  • Process request for pseudonymous user                    │
│  • Return clean JSON payload                                │
└─────────────────────────────────────────────────────────────┘
The Six Guarantees of Mediated Egress
Declared and DNS-Verified
The Butler's manifest explicitly declares a single public HTTPS origin (e.g. https://api.gymtracker.com). Before the submission can be reviewed, the developer must prove domain ownership by adding a_lifebutler-verification TXT record in their DNS zone. Life Butler periodically reverifies this record; if the record lapses, egress is severed immediately.
Staff Supervised Review
External endpoints undergo human review alongside manifest capabilities. Developers must provide a clear justification for what data is transmitted, why the integration requires external processing, and how deletion requests are handled.
Explicit, Revocable User Consent
Installing a Butler never silently enables network permissions. The host application displays an explicit consent prompt: "Gym Buddy transmits workout data to api.gymtracker.com". Users can inspect network permissions or revoke consent anytime in the Butler's settings.
Pseudonymous User Isolation
Developer servers never see your real Life Butler user ID, email address, or device identifier. The relay computes a stable pseudonymous subject hash:HMAC-SHA256(user_uuid, butler_secret) → sub_butler_9a8f...
Two Butlers from different developers cannot correlate the same human user across ecosystems.
Hardened SSRF & Request Sanitization
The edge relay strips all browser cookies, authorization headers, and caller user-agents. It resolves hostnames prior to connection, strictly rejecting private, loopback, or cloud-metadata IP ranges (AWS 169.254.169.254). Requests and responses are capped at 256 KB JSON with an 8-second timeout.
Cryptographic Signing & Auditability
Requests are stamped with X-LifeButler-Request-Id, X-LifeButler-Timestamp, and an HMAC-SHA256 signature using the Butler's signing secret. Call metadata (latencies, status codes, payload bytes) is visible to developers in the Developer Portal, while staff retain an instant kill switch to revoke egress.
How Developers Implement Remote Calls
Integrating remote calls requires three simple steps: declaring the origin in manifest.json, calling the bridge in your client bundle, and validating the signature on your server.
1. Declaring in manifest.json
{
  "name": "Gym Buddy",
  "version": "1.2.0",
  "permissions": ["tasks:read", "tasks:write"],
  "network": {
    "origin": "https://api.gymtracker.com",
    "justification": "Syncs completed workout tasks to your GymTracker member profile."
  }
}
2. Invoking the Bridge
// Inside your Butler bundle:
const response = await window.bridge.remote.call('/v1/workouts/sync', {
  method: 'POST',
  body: {
    workoutId: 'cardio-5k',
    completedAt: '2026-10-26T08:30:00Z',
    durationMinutes: 28
  }
});

console.log('Sync status:', response.status); // 200 OK
3. Verifying on the Developer Server
// On your backend (e.g. Node.js / Express):
app.post('/v1/workouts/sync', (req, res) => {
  const signature = req.headers['x-lifebutler-signature'];
  const timestamp = req.headers['x-lifebutler-timestamp'];
  const pseudonymousUser = req.headers['x-lifebutler-subject']; // e.g. "sub_butler_9a8f..."

  const expectedSig = crypto
    .createHmac('sha256', BUTLER_SIGNING_SECRET)
    .update(`${timestamp}.${JSON.stringify(req.body)}`)
    .digest('hex');

  if (signature !== expectedSig) {
    return res.status(401).json({ error: 'Invalid Life Butler signature' });
  }

  // Safely associate workout data with pseudonymousUser
  db.workouts.save({ userId: pseudonymousUser, ...req.body });
  return res.json({ success: true });
});
Under the Hood: Kafka-Only Microservice Isolation
To support this mediated egress securely without creating runtime coupling across internal services, we also codified our strict backend communication standard (ADR BACKEND-2026-10-25-kafka-only-service-communication):
- No Database Sharing: Every microservice (
developer-api,admin-api,developer-processor,admin-processor) strictly owns its schema. Cross-schema joins and shared database connections are decommissioned. - No Direct Internal REST: Inter-service coordination occurs solely through Kafka event topics using transactional outboxes. The egress relay receives origin approvals, quota changes, and kill-switch events as event streams, ensuring zero cascading downtime.
Building With Privacy as a Primitive
We believe you shouldn't have to sacrifice data sovereignty to use rich, connected tools. By enforcing mediated, authenticated, and pseudonymous remote calls, Life Butler gives developers the power of cloud backends while preserving our unwavering promise to users: your personal life remains yours alone.
Egress mediation is currently available in the Developer Portal Sandbox. Read the full spec in our Developer Documentation and start testing your integrations today.